Webinar: How malicious OAuth apps can lead to Google Workspace breaches
Material Security will host a webinar on September 23, 2026, featuring Rajan Kapoor and Rick Fitzgerald examining two attacks that used malicious OAuth applications and social engineering to breach Google Workspace environments.
Intelligence analysis by Qwen 2.5 (3B)
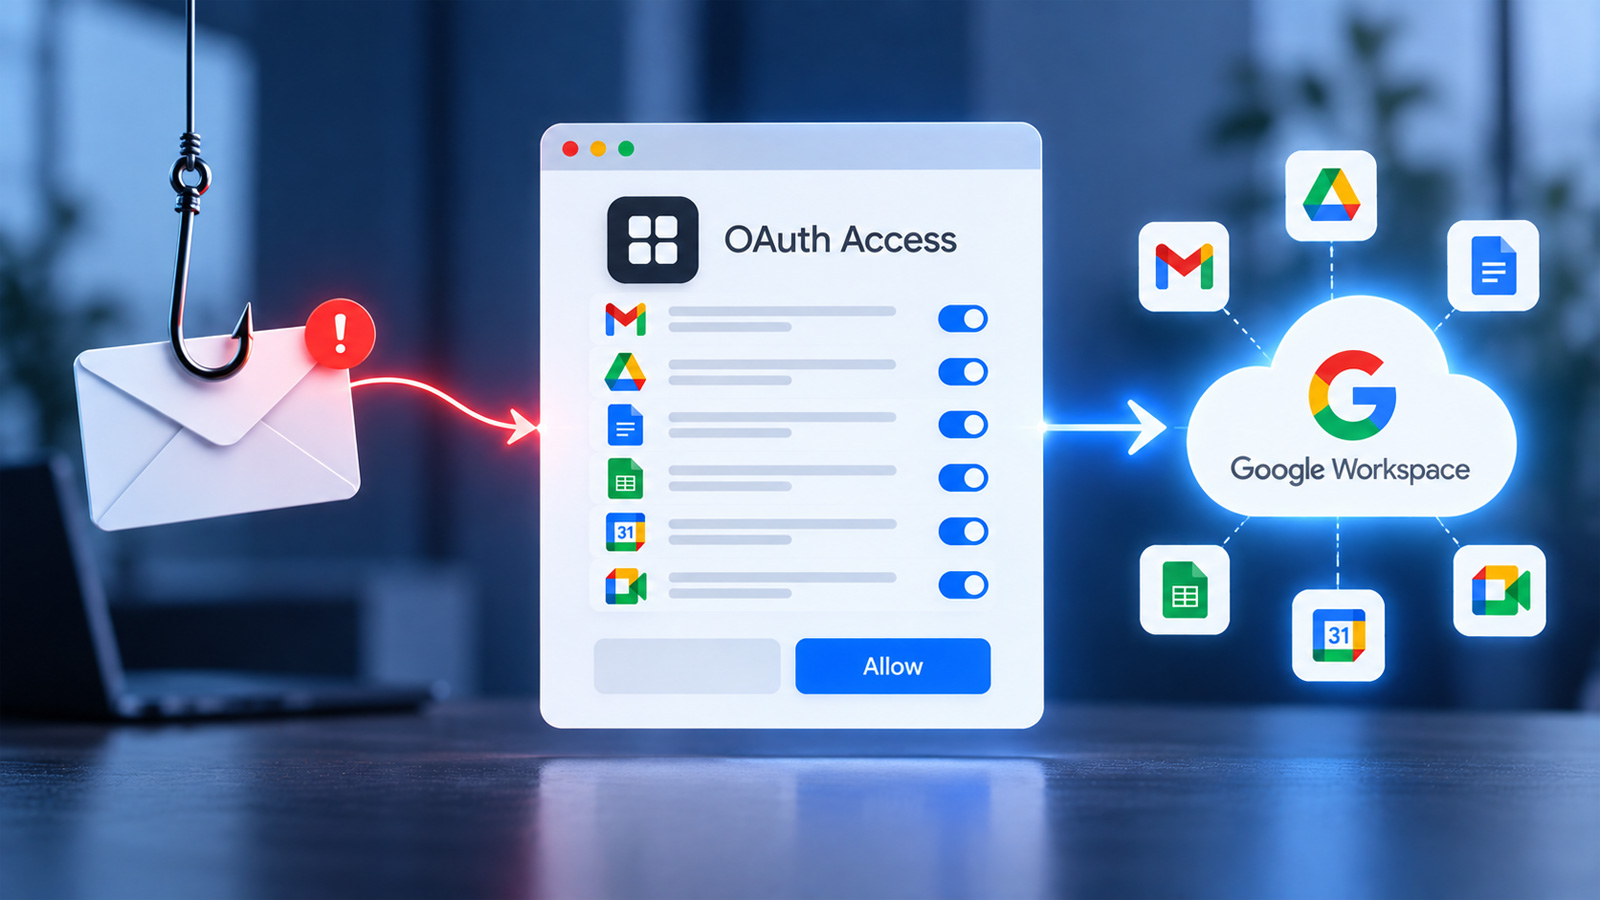
Material Security will host a webinar on September 23, 2026, to discuss attacks that used malicious OAuth applications and social engineering to breach Google Workspace environments.
Attacker tricks you into letting them use your Google Workspace account. They use something called OAuth to get access without you knowing. The webinar will teach how to spot this trick and what to do about it.
Analysis
Understanding OAuth Applications and Social Engineering
OAuth applications allow users to grant applications access to Google Workspace data and services without sharing their passwords. However, attackers can also abuse the authorization process by convincing users to grant permissions to malicious apps. Rather than stealing credentials, attackers can use social engineering to persuade a target to authorize an application, potentially providing access to sensitive information available through the permissions the user approved.
Two Attacks Examined
During the webinar, the speakers will break down how the two attacks unfolded, the weaknesses that allowed them to succeed, and the decisions organizations made during the critical first hours of the incidents. Attendees will also learn which security controls provide the greatest value for fast-growing organizations and what the speakers would prioritize if they were building a Google Workspace security program from scratch.
Practical Security Improvements
The webinar will cover practical security improvements organizations can implement quickly, ranked by effort and potential impact. Attendees will learn how to reduce their exposure to attacks that use malicious OAuth applications and social engineering.
Key points
- Attacker tricks users into letting them use their Google Workspace account
- OAuth applications allow access without sharing passwords
- Attacker uses social engineering to get users to authorize malicious apps
- Organizations need to understand which applications have access to their environment
- Attendees will learn practical security improvements to reduce exposure
Organizations can learn from these attacks and improve their security measures to prevent similar breaches in the future.
If organizations don't take the lessons from these attacks seriously, they could still be vulnerable to similar breaches.



