
bleepingcomputer.com
Ransomware has a new target. Is your backup ready?
Ransomware groups are targeting backups, making them a new threat. IT leaders need to secure their backups to prevent data loss.
Stories tagged “Ransomware.”
30 stories
Ransomware groups are targeting backups, making them a new threat. IT leaders need to secure their backups to prevent data loss.
Spanish police arrested a 16-year-old Romanian national in Alicante, suspected of being the main operator of the KillSec ransomware group, as part of an international operation.
ShinyHunters breaches Clop's data leak site, defacing it and stealing data. They threaten to extort Clop if they don't retract a threat to ShinyHunters.

ThreatsDay: New threats found in AI tools, exposed services, and software. 800+ flaws patched, insider SIM swaps, and 22 more stories.
Fintech company Revolut denies receiving direct contact despite multiple public ransom demands, including one for $3 million in Monero, following a customer data breach. Italian authorities are now investigating the incident, which allegedly involved a government email ac…
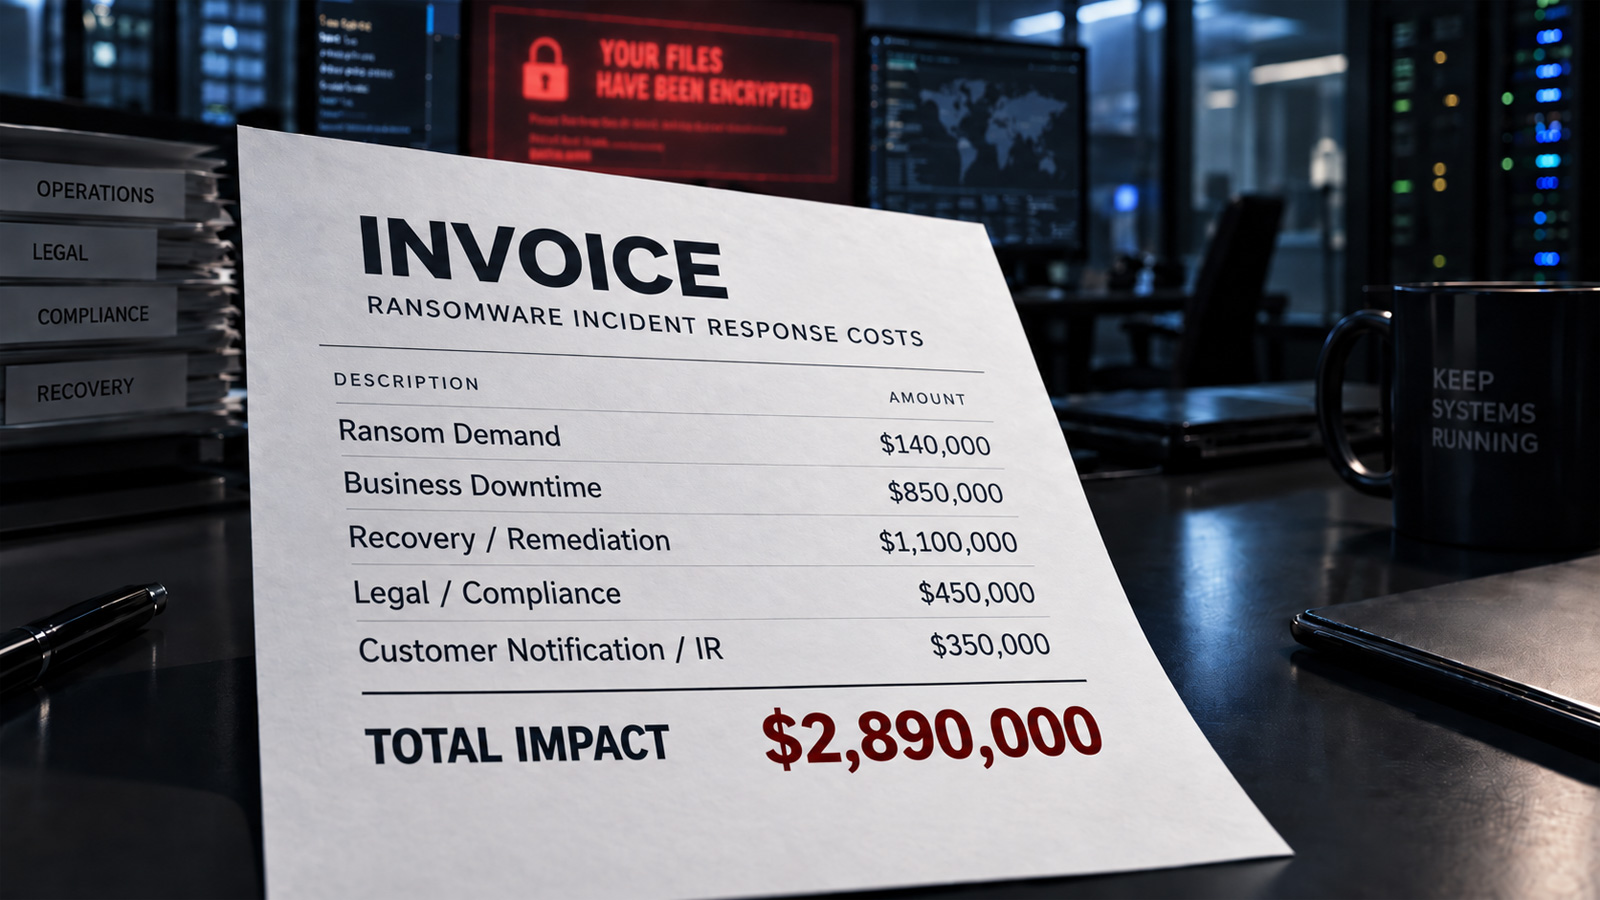
Ransomware attacks can be costly, but BCDR can help reduce downtime and recovery expenses.
CISA warns of ransomware gangs exploiting critical VMware vCenter vulnerability patched in July.
Cisco FMC vulnerabilities exploited by ransomware and state-sponsored hackers
CISA confirms ransomware gangs are exploiting WatchGuard Firebox firewall vulnerability, CVE-2025-14733, affecting Fireware OS 11.x and later.
Veradigm discloses a data breach affecting patients' personal data, including SSNs and email addresses, after a ransomware group claims responsibility.
Ransomware attacks on German authorities have increased, with 10% more cases in 2025 reported by the Federal Criminal Office. Consequences include service disruptions and delays in payments for citizens.

This ThreatsDay report details a range of sophisticated cyberattacks, including CEO phishing kits, large-scale Dropbox account hacks, and OAuth traps, alongside 17 other security incidents.
Berlin confirms data theft after Rhysida ransomware attack claims. City administration will not pay the attacker and is investigating the incident.

PaperCut has issued an emergency patch for a zero-day vulnerability actively exploited in its NG and MF print management software, affecting all versions. The company is investigating confirmed customer incidents and advises immediate access restriction for internet-expos…
The U.S. Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) has confirmed a "major incident" involving a compromised standalone system, following breach claims by the Qilin ransomware gang.
A suspected ransomware affiliate, operating as "Ransom Busters," is contacting victims before attacks become public, falsely claiming to be a recovery firm that can provide decryption keys and delete stolen data for a fee.
CISA, HHS, and FBI reported that the Medusa ransomware gang has breached over 500 critical infrastructure organizations in the United States since June 2021, an increase from a previous report.

A sophisticated JavaServer Pages (JSP) web shell, attributed to the Clop ransomware group, has been discovered targeting PTC Windchill and FlexPLM servers, designed to decrypt credentials and exfiltrate engineering data.

A ransomware affiliate calling itself Ransom Busters has been spotted proactively sending emails to victim organizations and claims to delete stolen data from ransomware groups' servers in exchange for a fee ranging from $20,000 to $60,000.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are exploiting a high-severity Windows Task Host vulnerability. The vulnerability, tracked as CVE-2025-60710, allows local attackers with basic user permissions to gain SY…
Philips and General Electric (GE) are investigating claims that the Clop ransomware gang breached their systems and stole data. The Clop gang has listed the companies on its leak site as part of a batch of 43 new victims likely targeted in data theft attacks.

A suspected Chinese-speaking APT is mass-exploiting a critical Broadcom VMware vCenter directory-traversal flaw (CVE-2026-59310, CVSS 9.8) to plant backdoors and stage ransomware across 361 victims in 47 countries.
Akira hackers disable EDR with Safe Mode, steal data but fail to encrypt. The attack occurred on August 4 after the hacker obtained initial access through an exposed SonicWall VPN device without multi-factor authentication (MFA).
The White House has signed a national security presidential memorandum that enables private security companies to apply for approval to hack foreign cybercrime organizations. The program will be overseen by executive directors designated by the Justice and Homeland Securi…
The best antivirus software to protect your computer in 2026
ZDNET experts put every product through rigorous testing and research to curate the best options for you. Our favorite antivirus software protects your PC, laptop, and mobile devices from malware without costing a fortune.

A federal judge in Alexandria, Virginia, sentenced Maksim Silnikau to 16 years in prison for creating and running Ransom Cartel, the ransomware-as-a-service operation he stood up in 2021.
Maksim Silnikau, the creator and administrator of the Ransom Cartel ransomware operation, was sentenced to 16 years in prison for his role in ransomware attacks against at least 18 companies worldwide.

The INC Ransomware operation has emerged as the dominant threat actor exploiting the recently disclosed security flaws in SonicWall Secure Mobile Access (SMA) 1000 series VPN appliances. Fixes for the vulnerability pair were released by SonicWall in mid-July 2026.
Coca-Cola has confirmed that hackers stole data from its dairy subsidiary, Fairlife, during a ransomware attack earlier this month. The company says it is still working to restore some of the impacted systems and operations, but most of the production in the U.S. has been…

Threat actors linked to the Cl0p ransomware campaign are exploiting flaws in internet-exposed PTC Windmill and FlexPLM deployments as part of a new data extortion campaign.