‘You have a meeting’: the calendar phishing scam growing exponentially
A new calendar phishing scam is rapidly increasing, tricking users into believing they have forgotten meetings or renewals, leading them to fake login pages for services like Google, Microsoft, or PayPal.
Intelligence analysis by Gemini 2.5 Flash
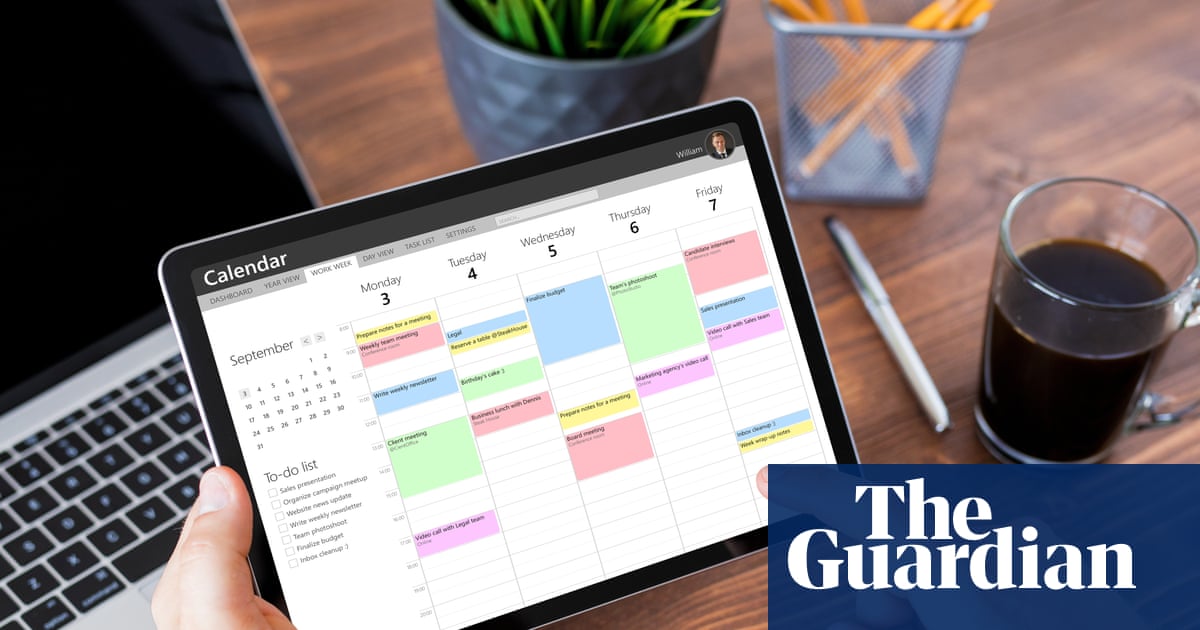
Scammers are exploiting the automatic invitation feature of calendar applications to bypass traditional email filters, making their phishing attempts appear more credible. These fake calendar entries prompt users to click malicious links or call fraudulent support numbers, ultimately aiming to steal personal login credentials and financial information.
Imagine someone secretly adding a fake playdate to your school planner, making it look like a real one. When you check it, there's a link saying 'click here for details.' If you click and type in your secret club password, you've accidentally given it to the trickster! That's what grown-ups are facing with their digital calendars, where sneaky people put fake meetings to steal their online passwords for things like games or shopping.
Analysis
The emergence and rapid proliferation of calendar phishing represent a significant evolution in cybercrime tactics, leveraging the inherent trust users place in their digital calendars. Unlike traditional email phishing, which often relies on users opening suspicious messages, calendar phishing exploits the automatic acceptance features of popular calendar applications like Google Calendar. This allows malicious invitations to appear directly alongside legitimate appointments, lending them a 'borrowed credibility' that makes them harder to discern as fraudulent.
Luke Wescott
Luke Wescott, a threat detection engineer at Sublime Security, highlights the alarming rate at which this scam is expanding, noting its "exponential growth." His observations underscore the novelty and effectiveness of this method, which circumvents typical security measures. Wescott points out that calendar apps can automatically add invitations without user acceptance, meaning scammers don't even need the victim to open an email. This passive infiltration makes the scam particularly insidious, as users are more likely to interact with something already present in their trusted calendar interface.
Max Gannon
Max Gannon, an intelligence analysis manager at Cofense, further elaborates on the sophistication of these attacks. He notes that some fraudsters are utilizing legitimate platforms, such as Zoom, to dispatch these deceptive invitations. This tactic not only makes the invites appear more authentic to recipients but also poses a significant challenge for advanced security software, including AI-backed blockers, to detect and filter. Gannon explains that blocking invitations from such platforms entirely would inadvertently block legitimate meeting requests, creating a dilemma for cybersecurity defenses.
Google Calendar
The article specifically mentions Google Calendar as one of the platforms susceptible to this scam due to its automatic invitation acceptance settings. The scam typically involves an email containing a calendar request, which, regardless of whether it's opened or lands in spam, can automatically populate the user's calendar. These entries often masquerade as urgent notifications, such as 'New voicemail received,' 'Payment receipt confirmation,' 'PayPal unusual activity,' or 'Your auto-payment will be processed within 24 hours.' The goal is to prompt the user to click a link embedded in the event description, leading to a fake login page for services like Microsoft, Google, or PayPal, or to call a fraudulent 'support' number to cancel a non-existent charge. Users are advised to disable automatic acceptance of invitations in their calendar settings and to treat all unexpected entries with extreme suspicion, deleting or reporting them as spam rather than declining, which could confirm their address is 'live'.
Key points
- Calendar phishing is a rapidly growing scam that exploits automatic invitation features in digital calendars.
- Scammers send fake meeting or renewal requests that appear directly in victims' calendars, often bypassing email filters.
- These deceptive entries lure users to fraudulent login pages for services like Google, Microsoft, or PayPal, or to scam support numbers.
- The scam gains 'borrowed credibility' by appearing alongside legitimate appointments, making it harder for users to identify.
- Users are advised to disable automatic invitation acceptance in calendar settings and to treat all unexpected entries with suspicion, deleting them rather than declining.
The exponential growth of calendar phishing, coupled with its ability to bypass advanced security filters and leverage trusted platforms, suggests a significant and escalating threat. This could lead to widespread credential theft, substantial financial losses for individuals and businesses, and a further erosion of trust in digital communication and scheduling tools.